GovWare 2026

Agentic speed, human approval. See Resolve live at Booth J37.

13–15 Oct · Sands Expo, SingaporeSee details

AgentShift-left · Agentic module

Agentic Code Analysis,from scan to merged fix

Scan source code, dependencies, infrastructure as code, Android packages, and container images. Review findings, create PRs in one click, and share reachability with WAF, DAST, and Resolve automatically.

  • SAST
  • SCA
  • IaC
  • APK
  • Container image scanning
Agentic Code Analysis · FlowContext → Axiler Resolve
Code
Scan
Review fix
Pull request
Reachable paths
Resolve
Create PR
Ship fixes from code review
CWE map
Compliance-ready finding context
Secrets
Detect and revoke leaked tokens
Agent sync
Reachability shared downstream

Capabilities

What Agentic Code Analysis does

SAST

Review findings with CWE context, then ship the fix as a PR

Every finding opens with severity, CWE and OWASP mapping, confidence, impact, and likelihood. Compare vulnerable code against the AI-suggested fix side by side, then create a pull request without leaving the SAST console.

  • CWE, OWASP, and risk metrics on every finding
  • Vulnerable vs suggested code in one panel
  • Create PR from the same review workflow
Agentic Code Analysis · SASTContext → Axiler Resolve
Finding
CWE mapping
Suggested fix
Create PR
Risk metrics
Resolve
SCA

Prioritize CVEs across your dependency tree

Scan summaries break down critical, high, medium, and low findings at a glance. Filter by package, CVE, or severity, then drill into installed vs fixed versions for every vulnerable dependency.

  • Scan summary with severity breakdown
  • Search by package, CVE, title, or file
  • Installed and fixed version on every row
Agentic Code Analysis · SCAContext → Axiler Resolve
Manifest
CVE scan
Severity
Fixed version
Upgrade PR

SBOM

Map your supply chain with an interactive dependency graph

Generate a software bill of materials for every scan. Explore components, licenses, and vulnerabilities, then switch to the force graph to see which packages sit on risky paths in your dependency tree.

  • 420+ components catalogued per scan
  • Color-coded nodes by severity
  • Drag, zoom, and click for component detail
Agentic Code Analysis · SBOMContext → Axiler Resolve
Repository
SBOM
Components
Licenses
Risky paths

Compliance mapper

Map AppSec scan results to the frameworks auditors ask for

Compliance Mapper rolls up your SAST findings against CIS, ISO 27001, OWASP Top 10, PCI DSS, and SOC 2 controls. See pass rates, failing controls, and where remediation will move the needle before audit season.

  • CIS v8, ISO 27001, OWASP, PCI DSS v4, and SOC 2 views
  • Pass, fail, and total counts per framework
  • Top failing controls linked back to scan findings
Agentic Code Analysis · Compliance mapperContext → Axiler Resolve
Scan findings
Compliance mapper
Frameworks
Failing controls
Audit report

No integration required

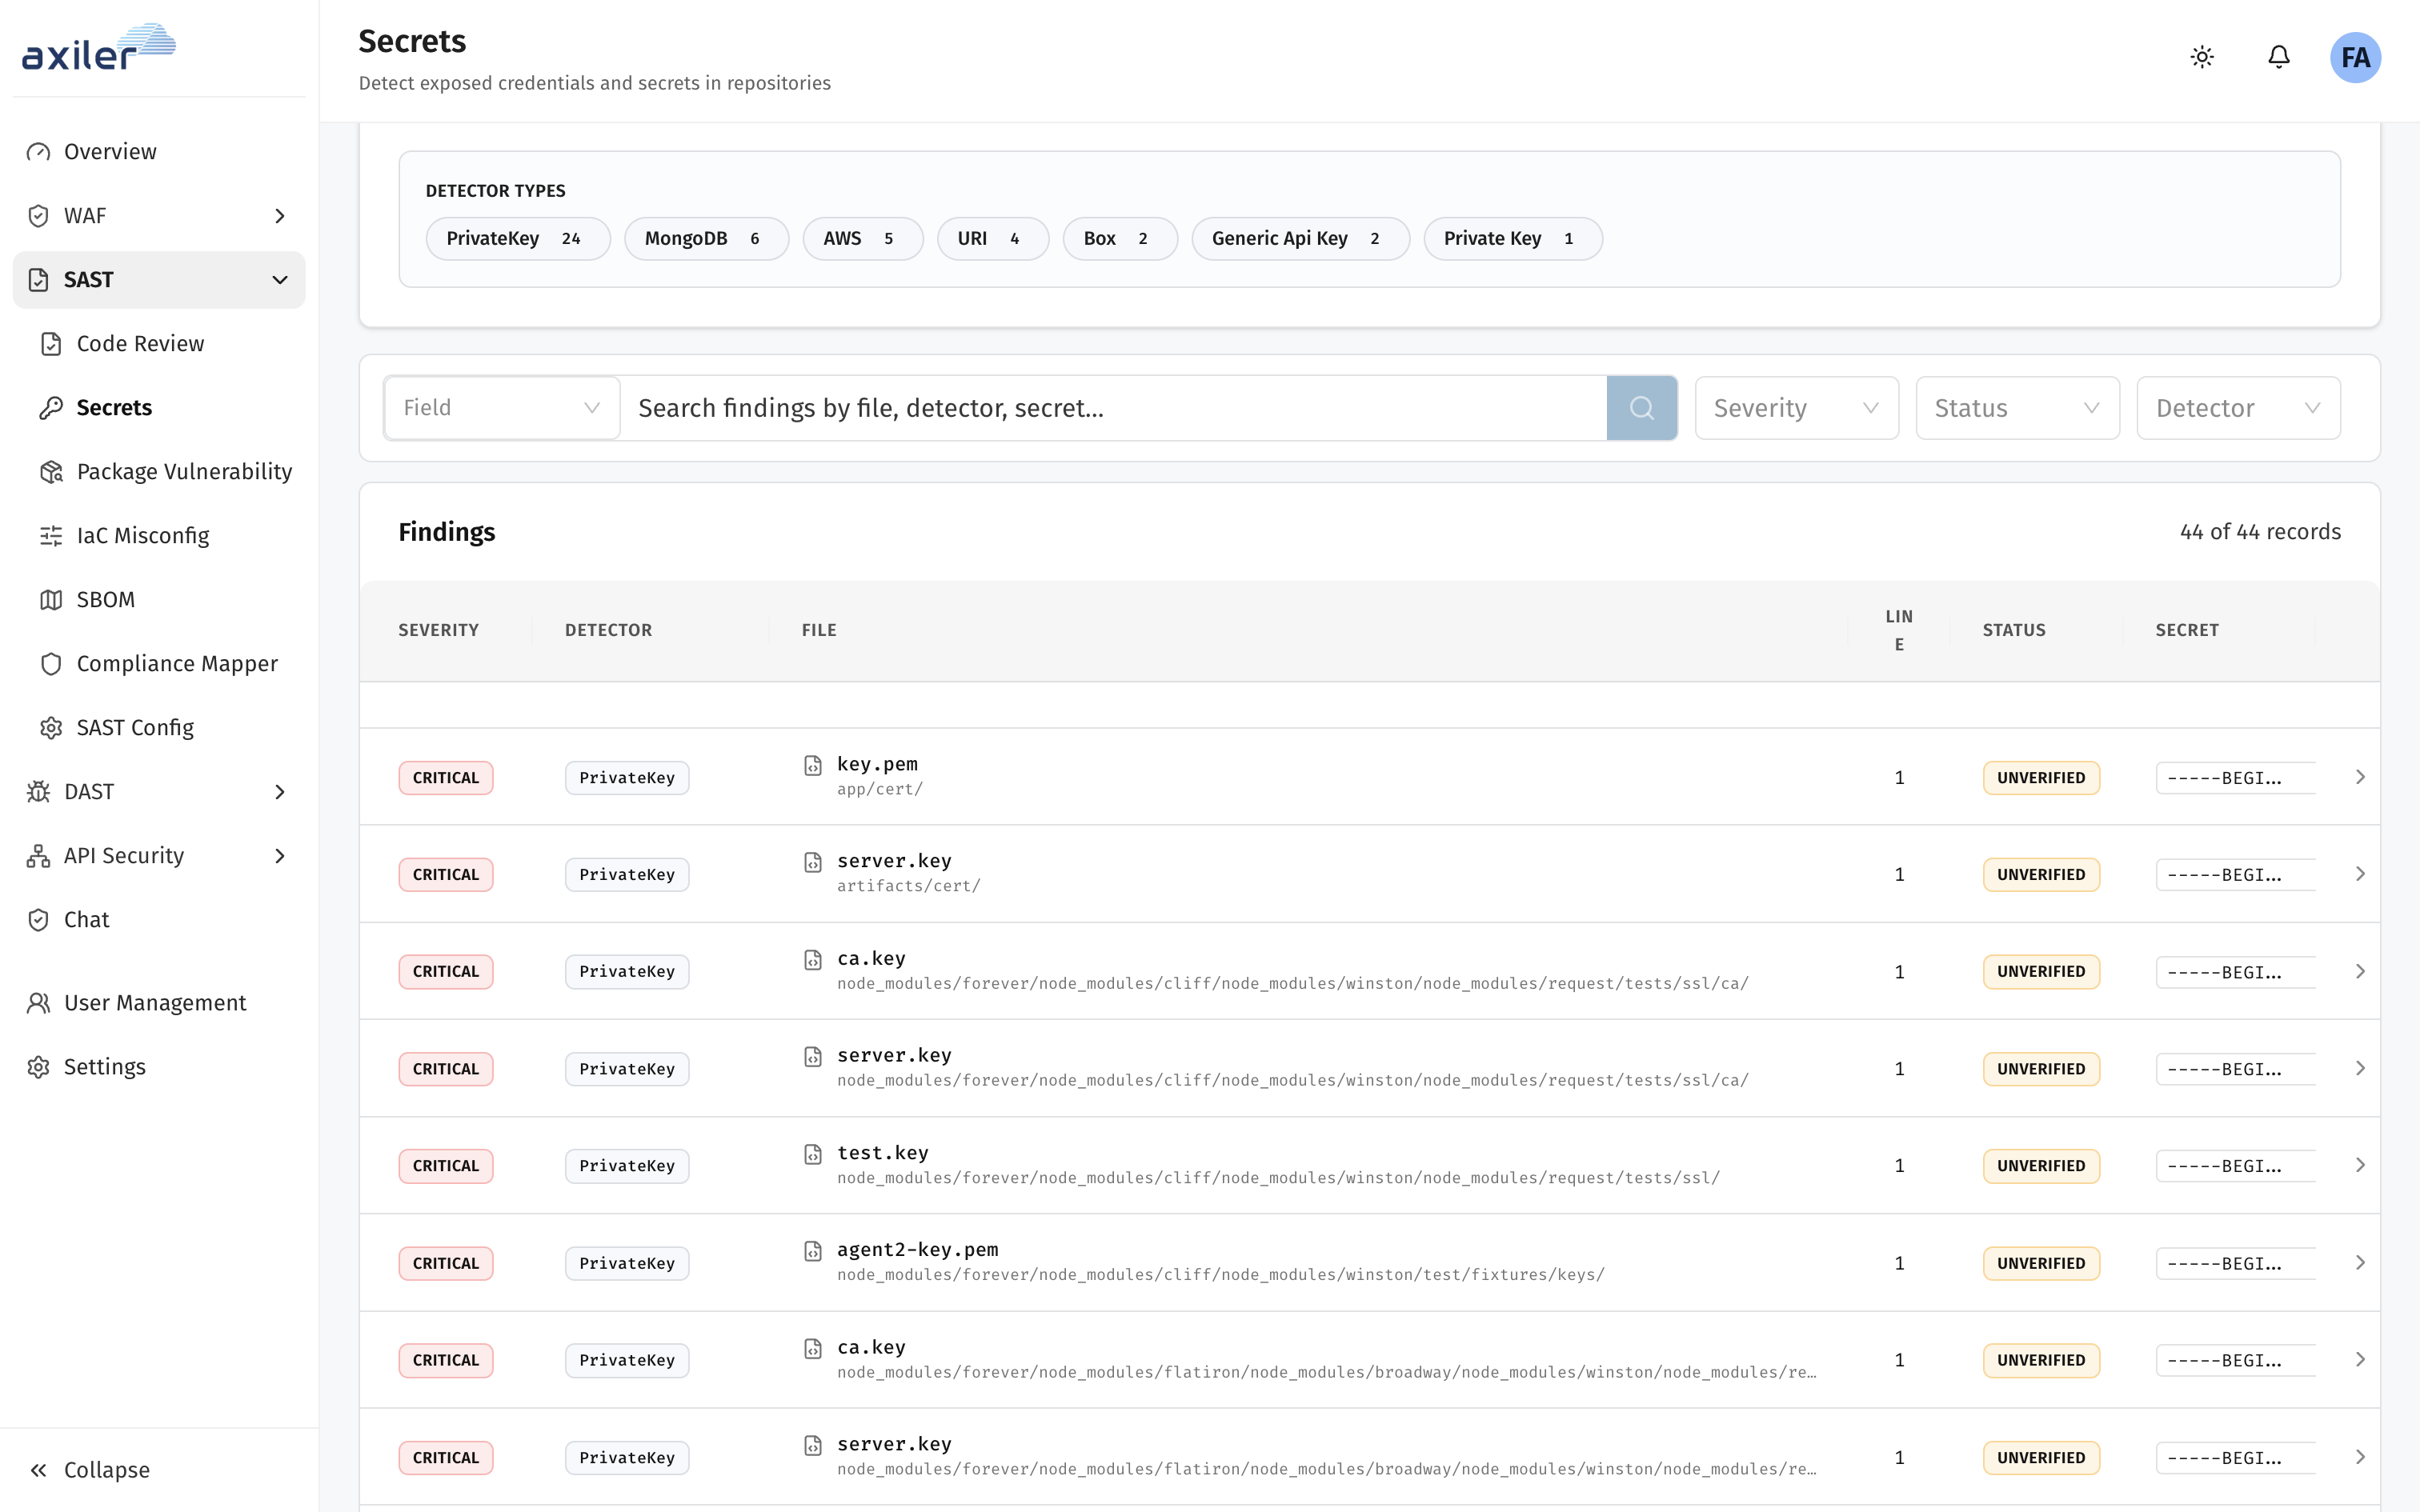
Secrets detection

Revoke leaked tokens without wiring up another tool

When Axiler finds exposed credentials in your repositories, you can revoke active tokens directly from the Secrets workflow. No AWS console integration, no vault connector, and no extra setup required.

  • Detect private keys, cloud credentials, database URIs, and API tokens
  • Revoke compromised tokens from the platform, not a separate tool
  • Filter by detector type, severity, and verification status

Built-in detectors

  • PrivateKey
  • AWS
  • MongoDB
  • URI
  • Generic API Key
  • Box
Secrets findings table showing PrivateKey, MongoDB, AWS, and URI detectors with critical severity and unverified status

SAST + WAF correlation

Turn live probes into code-level investigations

Connect Agentic Code Analysis with Agentic WAF and a runtime attack becomes a prioritized code review. Trace the probe to the files that matter, review the AI-generated fix, and open a PR while virtual patches keep production protected.

Runtime remediation

Virtual patches and generated WAF rules protect the vulnerable route while engineering reviews the fix. Traffic stays blocked at the edge from the moment the probe is confirmed.

Code remediation

Agentic Code Analysis maps the attack parameter to relevant source files, surfaces vulnerable vs fixed code, and lets you create a PR from the same correlated workflow.

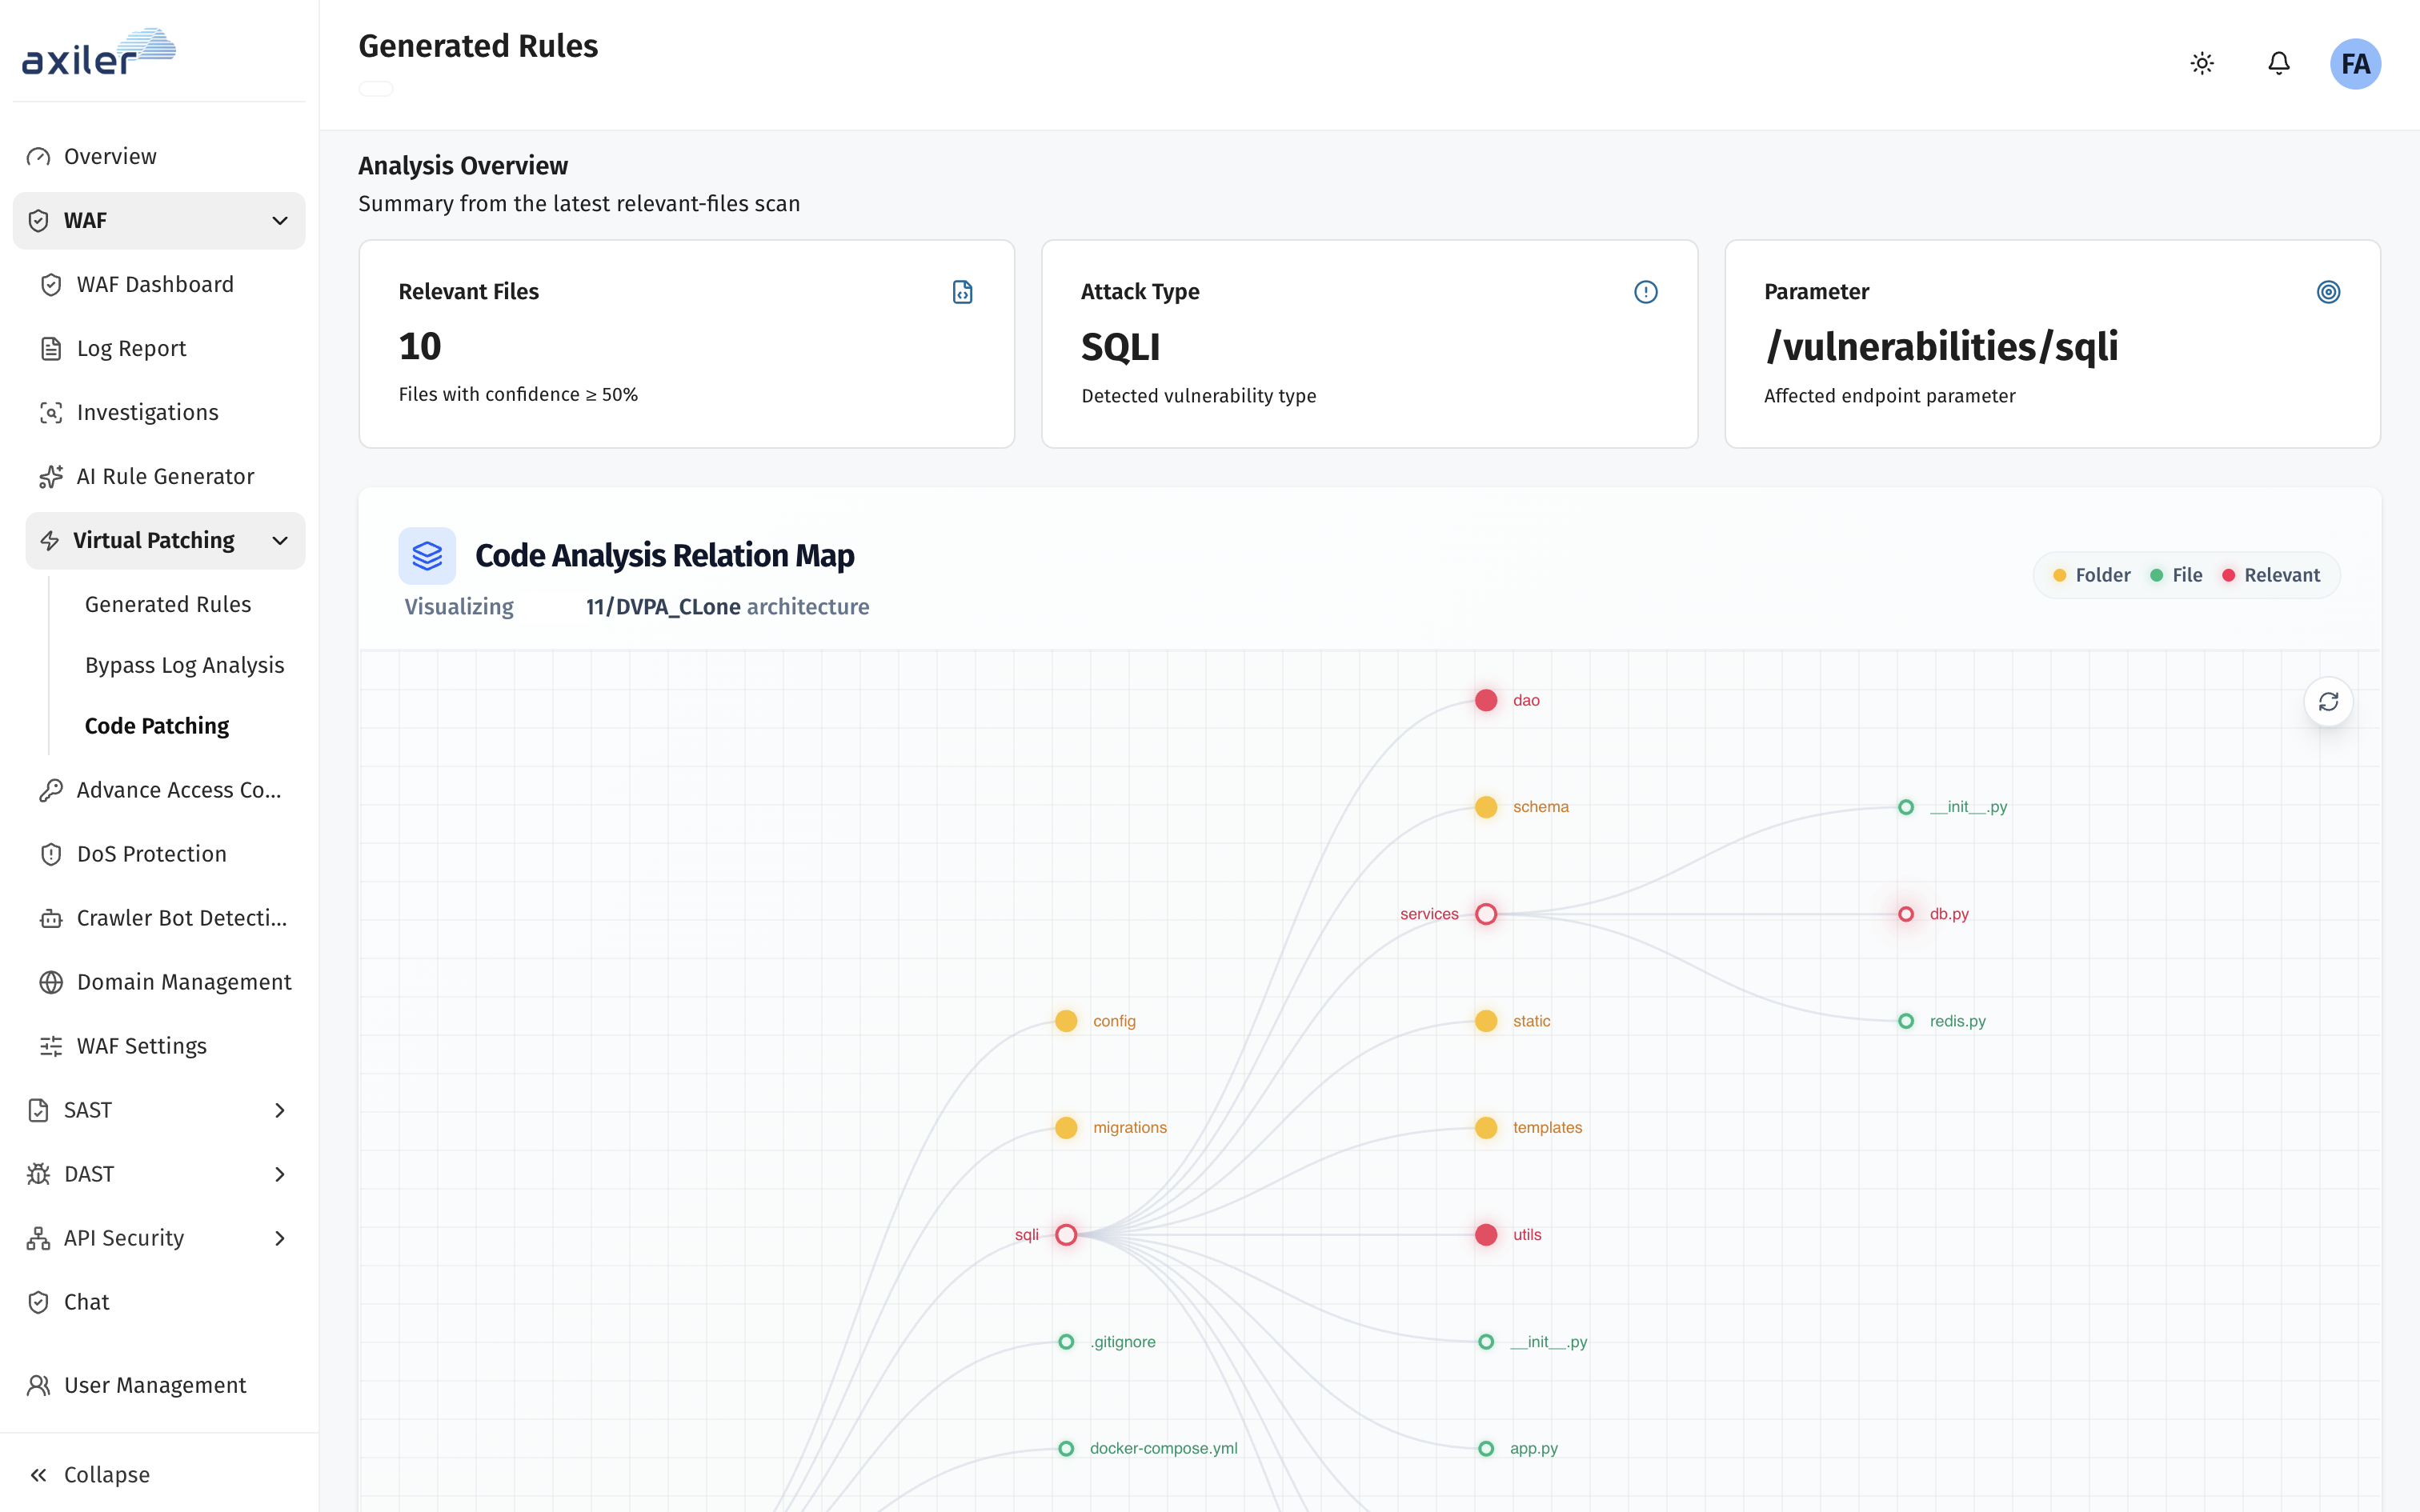
Map the probe to source files

A SQL injection hit on a live route is traced through your repo. The relation map highlights the services, DAOs, and utilities Agentic Code Analysis should prioritize for review.

Generated rules relation map linking a SQL injection WAF probe to relevant source files in the codebase

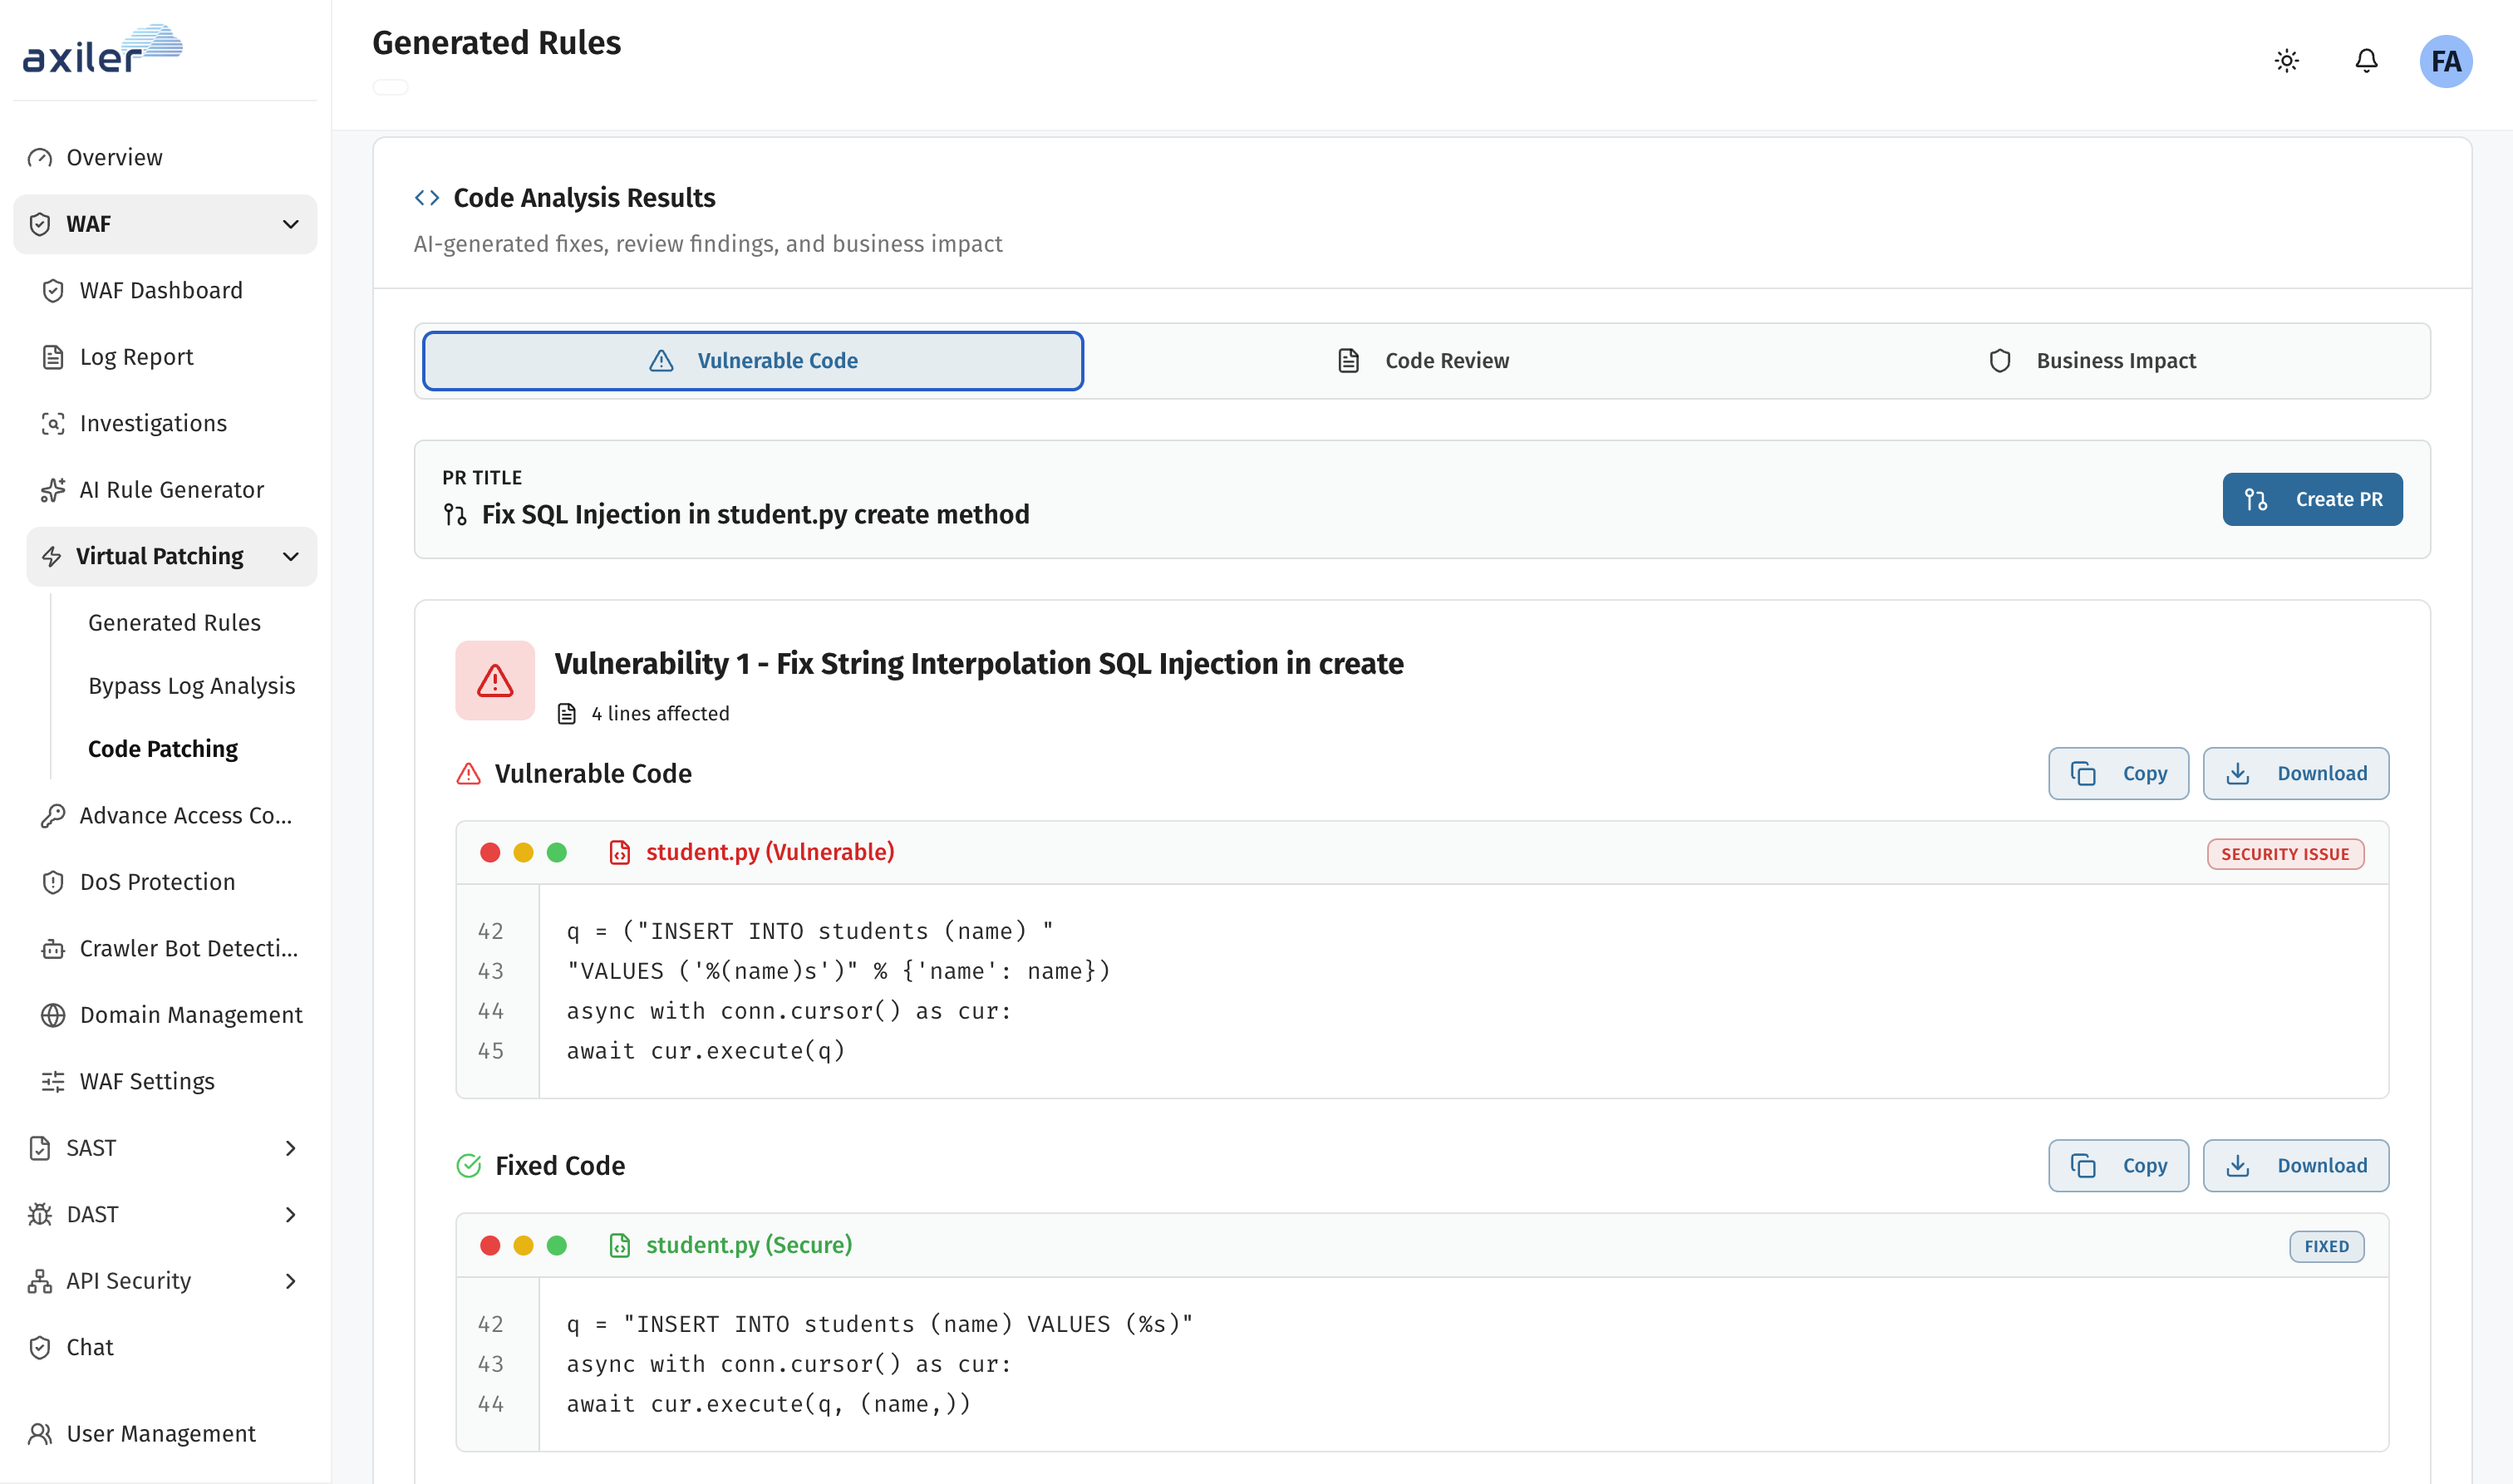
Review the fix and deploy to code

See vulnerable and patched code side by side, validate business impact, then create a pull request. The WAF probe that triggered the work stays linked through the entire review.

Code analysis results showing vulnerable and fixed SQL injection code with Create PR action

Available only when Agentic WAF is connected to your SAST workspace.

Explore Agentic WAF

Shift-left coverage

Scan code, dependencies, infrastructure, packages, and images

  • SAST

    Review source code findings before merge.

  • SCA

    Inspect vulnerable packages and dependencies.

  • IaC

    Scan infrastructure as code for misconfigurations.

  • APK

    Scan Android application packages.

  • Container image scanning

    Scan container images for known risks.

AppSec Suite

Code analysis is one agent in a connected stack

Agentic Code Analysis shares reachability paths with Agentic WAF, DAST, API Security, and Cloud Security. Axiler Resolve ranks what matters. Your team approves once, then fixes with full context.

Let's talk

Secure your codebase
with Athena.

See SAST, SCA, IaC, APK, and container image scanning in a demo tailored to your repos.

  • 30 minLive demo on your stack
  • ReviewCode findings with context
  • SOC 2Type II certified